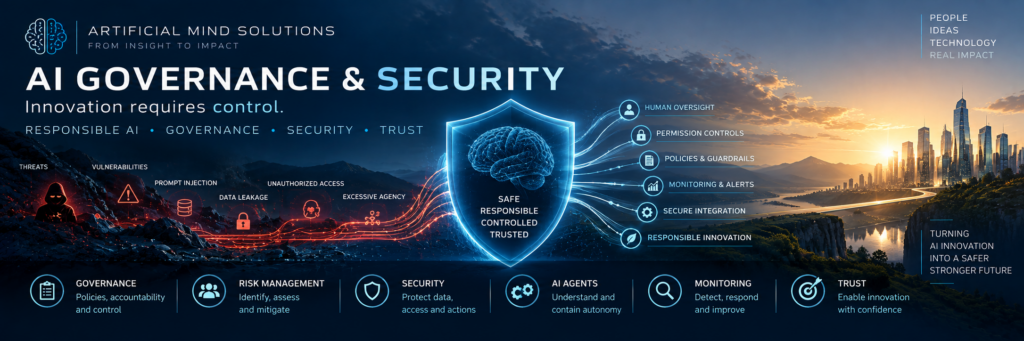
AI Governance & Security
Innovation requires control.
AI systems are becoming increasingly integrated with organizational data, applications, identities, APIs, workflows and infrastructure.
With Generative AI and Agentic AI, systems are also gaining greater ability to reason, decide and act.
This creates business opportunities — but also new forms of organizational and security risk.
Artificial Mind Solutions helps organizations implement AI while maintaining appropriate governance, accountability, security and control.
AI Governance
Effective governance should enable responsible innovation rather than create unnecessary bureaucracy.
We help organizations establish practical governance around:
- Accountability and decision rights
- Human oversight
- AI policies and guardrails
- Responsible AI
- Risk ownership
- AI lifecycle governance
- Vendor and model governance
- Data and access governance
- Monitoring and escalation
- Organizational controls
The objective is simple:
People must remain accountable for systems that increasingly act autonomously.
AI Security
Traditional application security remains essential, but increasingly autonomous AI introduces additional risks.
An AI system may interact with:
- Sensitive information
- User identities
- Permissions
- Business applications
- APIs
- Tools
- Memory
- RAG environments
- External services
- Other AI agents
The relevant security question therefore becomes not only:
“Can the AI model be manipulated?”
but also:
“What can happen if it is?”
From AI Influence to Real-World Effect
Artificial Mind Solutions evaluates the relationship between:
AI Influence → Authority → Effect
This helps distinguish model behaviour from actual organizational security impact.
We examine areas including:
- Excessive agency
- Permission boundaries
- Identity propagation
- Tool execution
- Prompt and data trust boundaries
- RAG security
- Agent-to-agent interaction
- Unauthorized actions
- Containment weaknesses
- Potential attack paths
- Realistic business impact
IASCF
Our AI security work includes assessments based on the Izzinosa Agentic AI Security & Containment Framework (IASCF).
IASCF focuses on the complete environment around AI systems rather than evaluating the model in isolation.
Findings are evidence-based and distinguish clearly between:
- Observations
- Potential vulnerabilities
- Reproduced vulnerabilities
- Demonstrated security effects
- Residual uncertainty
This gives decision-makers a clearer understanding of actual exposure and the actions required to reduce it.