RESPONSIBLE AI · ACCOUNTABILITY · AGENTIC AI ASSURANCE
Verantwoorde autonomie. Duidelijke verantwoordelijkheid. Aantoonbare beheersing.
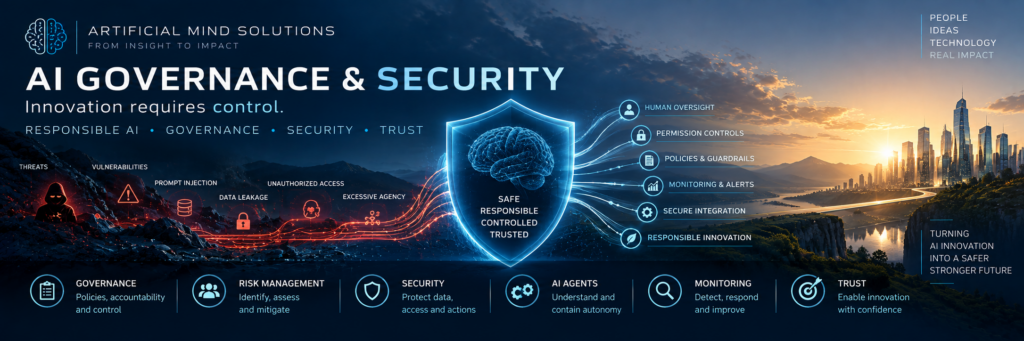
AI governance should enable useful AI transformation without sacrificing human accountability, operational trust or control. I connect organisational leadership, implementation and adoption with the security, privacy, legal and technical expertise required for each use case. Where agentic AI can act on business systems, we assess the boundaries, permissions and evidence needed to keep humans in control.
Onze focus en aanpak
Governance that supports AI adoption and execution
Start with clear business ownership and risk-based decisions. Identify which policies, legal requirements, safety boundaries, reviews and escalation paths are proportionate to the actual application. Embed these safeguards in the implementation plan with relevant technical and risk specialists, rather than making documentation or bureaucracy the end goal.
Agentic AI Assurance & Control Framework (AACF)
Ons Agentic AI Assurance & Control Framework (AACF) onderzoekt praktische vragen. Welke informatie mag een AI-agent inzien? Welke handelingen mag deze uitvoeren? Wie moet belangrijke wijzigingen goedkeuren? Kan een kwaadwillend bericht de agent verleiden regels te doorbreken? Kan achteraf worden nagegaan wat de agent precies heeft gedaan?
Illustratief voorbeeld: voordat een AI-assistent leveranciersbestellingen mag plaatsen, controleer je bestedingslimieten, regels voor menselijke goedkeuring en de registratie van iedere handeling. Dit is een testscenario, geen claim over een klantomgeving.
Beïnvloeding → Bevoegdheid → Gevolg
Een manipulatiepoging is niet automatisch een bewezen inbreuk. We onderscheiden waarnemingen, aannemelijke blootstelling, gereproduceerde kwetsbaarheden en aangetoonde gevolgen. Daarbij registreren we onzekerheden en beperkingen van het bewijs.
Onafhankelijk bewijs en reconstrueerbaarheid
Een AI-systeem mag niet als enige beoordelen of zijn eigen handelingen veilig waren. Bewaar registraties die een verantwoordelijke medewerker of een afzonderlijk systeem kan controleren, maak het mogelijk risicovolle handelingen te stoppen of te corrigeren en wijs een duidelijke menselijke eigenaar aan voor beslissingen en opvolging.
Focused agentic AI control assessments
For organisations adopting AI agents with tool and data access, AACF is a developing method to organise questions about permissions, trust boundaries, human approval, logs, containment and evidence. A scoped engagement may produce documented observations, prioritised risks, recommended safeguards and explicit limitations. Specialist testing is performed only within agreed authorisation and with appropriate expertise. This is neither a certification nor a claim of exhaustive security verification.
Put proportionate controls around the AI work that matters
Discuss how governance can support a wider AI transformation, or request a focused conversation about an AI-agent control question. We will clarify your business context and involve the relevant specialists where needed.
 Dutch
 English